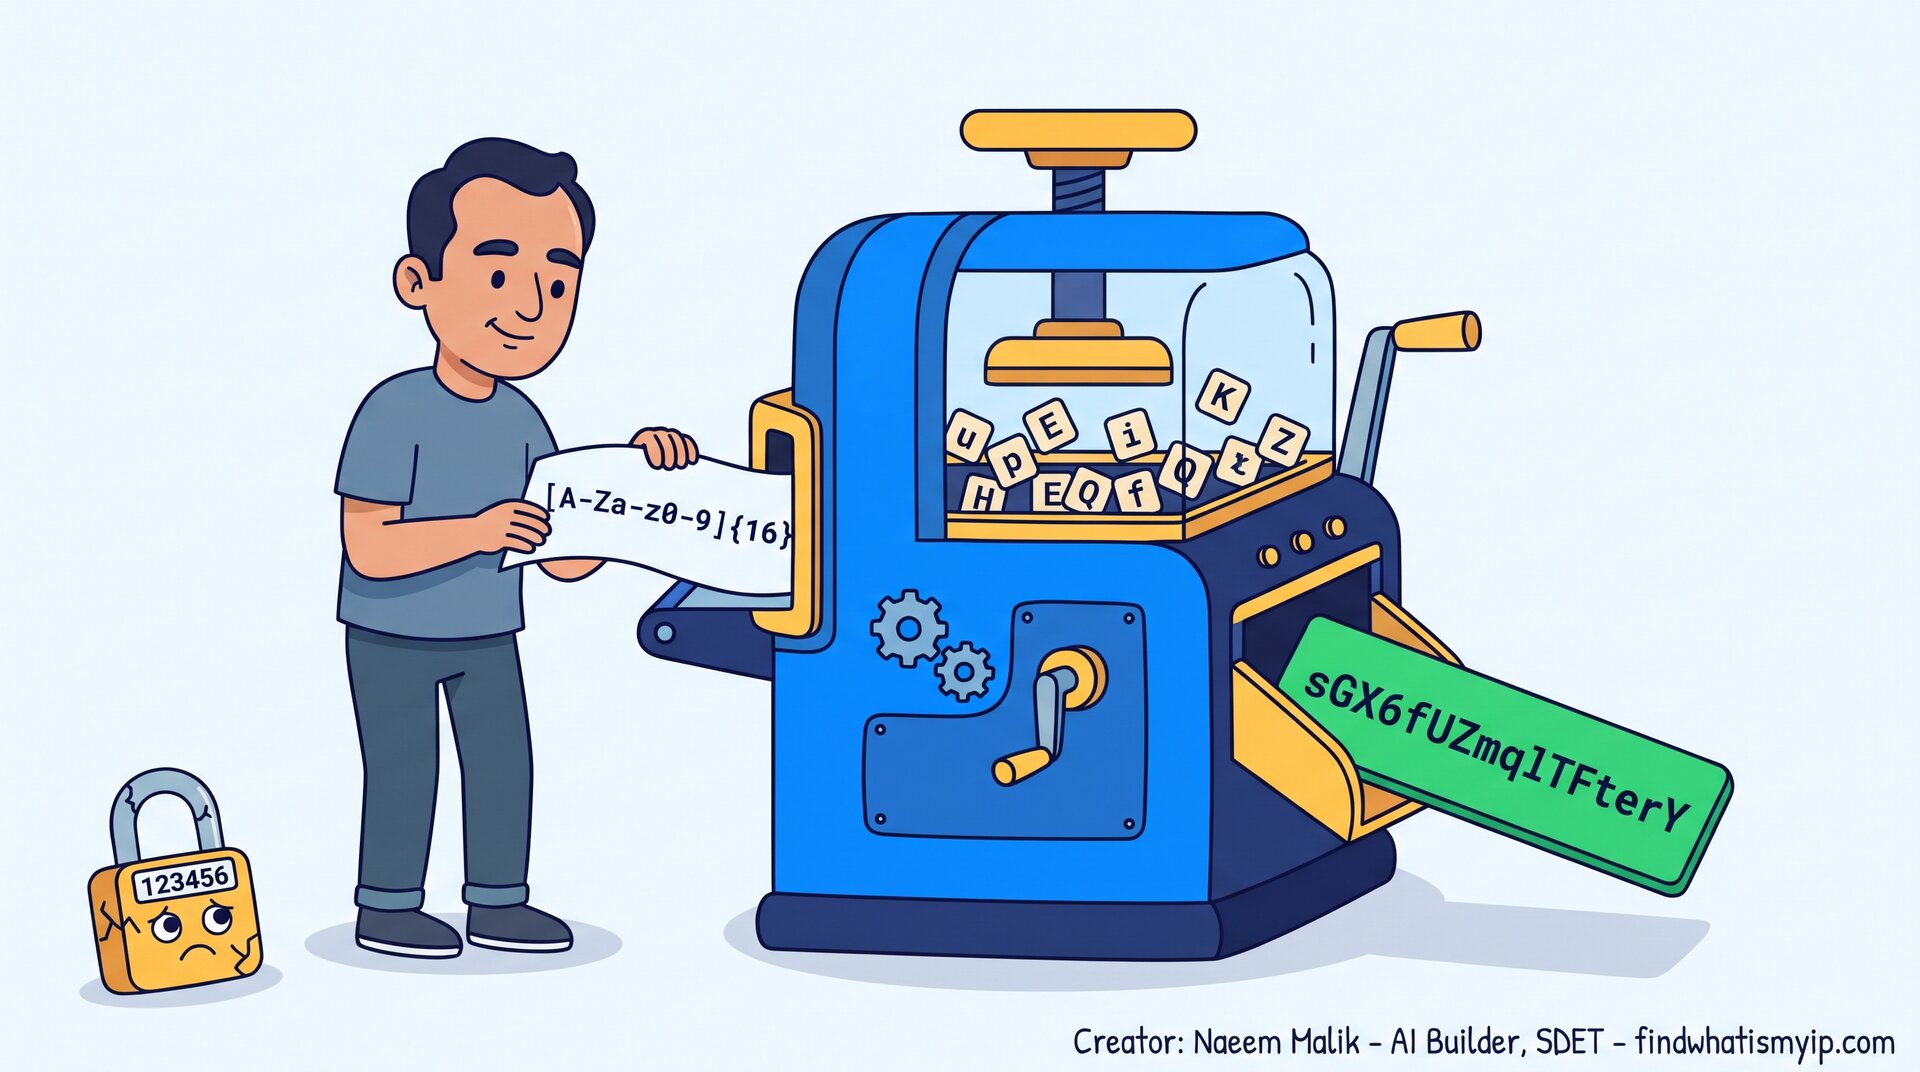
Some websites accept any password. Others want exactly 12 characters, two digits, only a couple of allowed symbols and a capital letter first. A generator that only offers a length slider and four checkboxes makes you keep clicking until a lucky one happens to fit.
I have added two ways to fix that to the free Strong Password Generator: you can set exactly how many uppercase letters, lowercase letters, digits and symbols you want, or you can describe the whole password with a regular expression and get one that matches. This post explains both, what each pattern is worth in bits of strength, where the limits are, why admins will find it useful, and why weak passwords keep causing real breaches, with recent examples.
What is new on the password generator
- A mode switch. Length & characters is the classic mode. Regular expression lets a pattern decide everything. Both Generate buttons follow whichever mode is selected.
- Per-type counts. A number box beside each character type sets how many characters of that type you get.
- Pattern mode with example patterns, live syntax checking as you type, and clear messages for anything unsupported.
- A length readout under the password, which matters in pattern mode because the pattern, not the slider, sets the length.
- A block list (“Don't Use These Passwords”) that applies in both modes.
Mode 1: choose exactly how many of each character
In Length & characters mode, each ticked type has a number box next to it. By default the length is split 60% letters (half uppercase, half lowercase) and 40% digits and symbols (half each), so you start with something sensible without typing anything:
| Length | Uppercase | Lowercase | Digits | Symbols |
|---|---|---|---|---|
| 12 | 4 | 4 | 2 | 2 |
| 16 | 5 | 5 | 3 | 3 |
| 20 | 6 | 6 | 4 | 4 |
| 64 | 19 | 19 | 13 | 13 |
The rules the boxes follow:
- Move the length slider or tick or untick a type and the numbers are recalculated. Untick a type and its box is greyed out and shows 0; the split is shared among the types that remain.
- No box can go above the password length, and the password is never longer than the length you set, whatever you type. If your numbers add up to too much, the largest one is trimmed. If they add up to too little, the gap is filled at random.
- Every ticked type gets at least one character.
- The characters are shuffled, so the types are not grouped together.
- After you generate, the boxes show what was actually used.
One honest trade-off: fixing the counts removes a few bits of strength compared with drawing every character from the full set. For a 16-character password with the default split that is about 96 bits instead of about 103, which is still far beyond anything that can be brute-forced.
Mode 2: generate a password from a regular expression
A regular expression, or regex, is a compact way to describe the shape of a string. Normally you use one to check whether text fits a shape (the regular expression for an IP address is a classic example). Pattern mode runs it the other way: you give the shape, and the tool produces a random string that fits it.
Select Regular expression, type a pattern, and press Generate. The
default pattern, [A-Za-z0-9]{16}, means “16 characters, each
a letter or digit.” In this mode the pattern decides the length and the
characters, so the slider and character options are hidden. The block list and
strength meter still work.
The syntax it understands
| Write this | It means |
|---|---|
[a-z] [A-Za-z0-9] [!@#$%] | One character from the set or range |
[^a-z0-9] | One character not in the set (printable ASCII only) |
\d \w \s . | A digit, a letter/digit/underscore, a space, any printable character |
{6} {4,8} | Exactly 6 / between 4 and 8 of the thing before it |
? * + | 0 or 1 / any number / at least one (open-ended repeats add at most 8 extra) |
( ) (?: ) | Group things so a repeat applies to all of them |
cat|dog | Either one, chosen at random |
\. \- | A literal character that would otherwise mean something |
Recipes, with what each one is worth
Every character drawn from a set of N options adds log2(N) bits of strength, and anything fixed in the pattern adds nothing. These are real outputs from the tool; the right-hand column is that arithmetic.
| You need | Pattern | Example result | Strength |
|---|---|---|---|
| 16 letters and digits | [A-Za-z0-9]{16} | sGX6fUZmqlTFterY | ~95 bits |
| 20 characters with symbols | [A-Za-z0-9!@#$%^&*]{20} | F&v@1oe*61v3&QK^oE87 | ~123 bits |
| Product-key style | (?:[A-Za-z0-9]{5}-){3}[A-Za-z0-9]{5} | aRBac-Xd5Wc-QgfGm-Gp0uw | ~119 bits |
| Four dashed blocks, lowercase | (?:[a-z]{4}-){3}[a-z]{4} | ybap-walh-zbvv-ddyi | ~75 bits |
| Capital first, then digits, ends in a symbol | [A-Z][a-z]{5}-[0-9]{4}-[a-z]{5}[!@#$%] | Qzlfqx-1304-mmlac@ | ~67 bits |
| A 6-digit PIN | [0-9]{6} | 229131 | ~20 bits |
| Two letters and six digits | [A-Z]{2}[0-9]{6} | UR763292 | ~29 bits |
A 6-digit PIN has only a million possibilities, which is fine behind a lockout after a few wrong tries and useless anywhere an attacker can guess freely. Treat anything under about 60 bits as a convenience, not as protection.
What not to do
It is tempting to bake words into a pattern, like
(?:correct|horse|battery|staple)[0-9]{4}. It produces
battery2231 and looks like a password, but it has only 4 ×
10,000 possible results: about 15 bits, which falls in seconds. Literal text and
short choice lists add almost nothing. Put the randomness in long runs of
characters, not in the fixed parts. If you want memorable words, use the
passphrase generator, which draws words
from a 7,776-word list (why passphrases
work).
What a pattern cannot do
Patterns cannot say “at least one of each type, anywhere.” That needs lookaheads, which the generator does not support. You can write the structure out (as in the capital-first recipe above), but each type then sits in a fixed position. When a site simply wants an uppercase letter, a digit and a symbol somewhere, use Length & characters mode: every ticked type is guaranteed at least one character and they are shuffled.
Limits and safety
- Everything runs in your browser. The pattern and the
result are never sent anywhere or stored. Randomness comes from
crypto.getRandomValues. - Size limits: a pattern can be 200 characters long, a single repeat count can be at most 128, and the password can be at most 256 characters.
- Not supported (you get a clear message): lookaheads and
lookbehinds, backreferences, named groups,
\b, flags, and^or$anywhere except the very start and end. - Your pattern is never run against text. The browser only checks it for syntax errors. That matters because some patterns make a regex engine backtrack for ages; the generator avoids that class of problem entirely, and complex patterns stop with a “too complex” message instead of freezing the page.
- Printable ASCII only for
.and negated sets like[^a-z].
Why this helps admins
If you run systems, you generate passwords all day, and they rarely come with the same requirements twice. Pattern mode and exact counts are built for that:
- Match a policy exactly. Need 16 characters with 4 digits and 2 symbols? Set the counts and the length stays at 16, whatever you type.
- Survive picky systems. Some legacy applications, device
consoles and config files choke on symbols.
[A-Za-z0-9]{24}gives you letters and digits only, still about 143 bits. - Passwords you can read down a phone line. Leave out the
look-alike characters
I,O,l,0and1with[A-HJ-NP-Za-km-z2-9]{16}(57 possible characters, about 93 bits), for exampleNZhQ9ozGbtCdY2pX. - Fixed-format credentials. Dashed licence-style keys,
a fixed-length Wi-Fi key (WPA2 allows 8 to 63 printable characters, so a
long
{n}works well; pair it with the Wi-Fi QR code generator), or test accounts that must all look alike. - See the length. The page shows how many characters the result has, so you can check it against a field limit before pasting.
- Respect your banned list. Paste your organisation's banned passwords into the “Don't Use” box and the generator will never return one of them.
- Nothing leaves the browser. The pattern and the password are not sent to the site or stored, so generating a credential here does not create a copy anywhere you do not control.
A practical habit: generate it, copy it straight into your password manager or secrets vault, and do not paste it into a ticket or chat. A generated password you then share in plain text is only as safe as the channel.
Which mode should you use?
Use Length & characters for everyday passwords and for sites that just require a mix of types. Use Regular expression when a system wants a precise format (an app code, a Wi-Fi key with a fixed layout, a dashed licence-style string, a test account with a specific shape). In both cases, store the result in a password manager, make it long, and use a different one for every account. The ultimate password security guide covers the habits that matter more than any generator setting, and the history of passwords shows why the rules look the way they do.
Why strong passwords matter
Attackers rarely “hack” their way past a login. They log in. They try lists of the most common passwords, replay passwords leaked from other sites, or use credentials stolen by malware on someone's laptop. A weak or reused password turns all three into a one-step attack, and automated tools run through millions of guesses without anyone watching. That is why the numbers earlier in this post matter: a 6-digit code has about a million possibilities, while a 16-character random password of letters and digits has about 5×1028.
Weak passwords persist because they are easy: people reuse one password everywhere, factory defaults are never changed, old accounts are forgotten rather than removed, and shared admin or service accounts get a quick “temporary” password that stays for years. A generator removes the human from that choice. The cases below show what happens when nobody does.
Recent breaches that started with a password
Details below come from public reporting; where something is an allegation or unconfirmed, the text says so.
Denmark's national person register (September–October 2026)
Denmark disclosed in early October 2026 that its central person register
(the CPR register) had been used to pull about 8.8 million records. The
attacker did not break into the government database itself: they used
accounts belonging to a private company with legitimate access, Pays ApS of
Odense. The newspaper Politiken reported that at least three of that company's
accounts, including an administrator account, used the password
123456. Authorities had not officially confirmed the password
detail at the time of the reporting, and police are investigating, so treat it as
reported, not proven. What is established: the misuse was noticed on 2
October, after an unusually high invoice showed the company had run far more
searches than normal, and its access was cut off. There are two lessons here:
one weak credential at a supplier can open a national register, and the
alarm here was a bill, not a security alert. See the
Copenhagen Post report.
Colonial Pipeline (2021)
Attackers got into Colonial Pipeline's network on 29 April 2021 through one VPN account that was no longer needed and had no multi-factor authentication. Mandiant's Charles Carmakal said the account's password was later found in a batch of leaked passwords, and that it was reused on other sites, though he said investigators may never know exactly how the attackers obtained it. He later described the password as “relatively complex.” Ransomware shut the pipeline down in May, and the company reportedly paid a ransom of about $4.4 million. The lesson: complexity did not help once the password was reused and nothing else stood in the way. Sources: TechRadar, TechRadar (follow-up).
23andMe (2023)
Attackers used credential stuffing, replaying usernames and passwords leaked from other sites, to get into about 14,000 accounts (roughly 0.1% of customers). Because those accounts were linked through the DNA Relatives feature, the company later said the personal data of about 6.9 million people was affected. 23andMe blamed customers' recycled passwords, a framing that plaintiffs' lawyers disputed, and it made two-step verification mandatory afterwards. The lesson: your reused password is a risk to people you are connected to, not only to you. See NBC News.
Snowflake customer accounts (2024)
Mandiant tracked a group that stole data from customer environments on the Snowflake cloud platform, with about 165 organisations notified. It reported that the cause was not a flaw in Snowflake's own systems: every incident it investigated traced back to compromised customer credentials, many taken by infostealer malware, in some cases years earlier, never rotated, on accounts without MFA and without any network allow-list. Ticketmaster was reportedly among the victims. The lesson for admins: old credentials are a liability, so rotate them, require MFA and restrict where logins may come from. See Mandiant's write-up.
Mirai and the Dyn outage (2016)
The Mirai botnet scanned the internet for cameras and video recorders still using factory-default logins (it carried a list of roughly 60 username and password pairs), and used the devices it took over to flood the DNS provider Dyn on 21 October 2016, knocking many well-known sites offline. The device maker Xiongmai said most takeovers were possible because owners had not changed the default passwords. The lesson: a default password is not a password. See Krebs on Security.
The Louvre: a password reported to be “LOUVRE” (unconfirmed)
After the October 2025 jewel theft at the Louvre, French press reported on an older security audit by the national cybersecurity agency ANSSI, dating from 2014, which reportedly found that typing “LOUVRE” was enough to get into a video-surveillance server. This one is not confirmed as a current weakness: the reporting does not establish that the password was still in use at the time of the theft, or that it played any part in it, and ANSSI said the audit cannot be considered representative of the museum's current security. The theft itself was physical, not a hack. It is included here only because it shows how easily the name of the thing becomes its password. See TechRadar.
What these cases have in common
- A single credential was enough. Nothing else stood in the way.
- The weakness was reuse, a default or a guessable value, not a clever exploit.
- The account was often a supplier, legacy or service account that nobody was watching.
- Detection came late: days or years afterwards.
What to do about it
- Give every account and service its own long, random password, generated rather than invented, and keep it in a password manager or vault.
- Turn on multi-factor authentication, especially for VPN, admin and supplier accounts.
- Change every default credential on devices and software before they go live.
- Remove or disable accounts nobody uses, and rotate credentials that must stay.
- Watch for unusual volume (searches, logins, data pulled) and limit where logins can come from.
What is a strong password policy, and how do enterprises enforce it?
A password policy is the written set of rules an organisation sets for how passwords are created, stored, changed and protected. A strong password policy is one that actually makes passwords hard to guess or steal, rather than one that just looks strict. The breaches above are what happens when the policy is missing, ignored or never applied to supplier, legacy and service accounts.
What a policy usually contains
- Minimum length (and a maximum high enough not to block long passphrases).
- Banned passwords: common words,
123456-style values, the company name, and passwords known from previous breaches. - No reuse: across systems, and a history so a user cannot flip back to an old password.
- Lockout and throttling after repeated failed attempts.
- Multi-factor authentication for remote, admin and supplier access.
- Rules for service and shared accounts: unique, generated, stored in a vault and rotated.
- A safe reset process and what to do after a suspected compromise.
Old rules versus current guidance
For years the standard recipe was “8 characters, one capital, one number, one symbol, change it every 90 days.” Current guidance has moved away from that. NIST's digital identity guidelines (SP 800-63B, revision 4, published in 2025) favour length over complexity: a longer minimum when a password is the only authenticator (15 characters, or 8 when it is one factor among several), accepting very long passwords (at least 64 characters), no mandatory composition rules, checking new passwords against lists of compromised and trivial values, and changing a password when there is evidence of compromise rather than on a fixed schedule. Other frameworks set their own numbers: PCI DSS v4.0.1 (requirement 8.3.6), for example, requires at least 12 characters (8 only where a system cannot support 12) with both letters and digits, from 31 March 2025. Check the current text of any standard you must meet. See NIST SP 800-63B-4 and a PCI DSS 4.0 summary.
How enterprises enforce it
A policy on paper protects nothing. Organisations enforce it in the systems people log in to, so a weak password is rejected before it exists:
| Policy element | How it is typically enforced |
|---|---|
| Length, complexity, history, expiry | The directory or identity provider rejects non-compliant passwords at creation and change time: Active Directory domain policy through Group Policy, with fine-grained policies for specific groups such as admins, and the equivalent settings in cloud identity services. |
| Banned and breached passwords | Password-protection features check every new password against a global list plus a custom list of your own words. Microsoft Entra Password Protection does this for cloud accounts and, with an agent, for on-premises Active Directory. It applies when a password is changed or reset. |
| Lockout and throttling | Failed-attempt limits and lockout durations in the same policy, plus rate limiting and alerting on the login endpoints. |
| Multi-factor authentication | Conditional-access rules and single sign-on make a second factor mandatory for VPN, admin and external access. |
| Service, shared and admin accounts | A privileged-access or secrets vault generates unique passwords, hands them out on demand, records who used them and rotates them automatically. |
| Monitoring and proof | Login logs and alerts for unusual activity, periodic reviews that remove stale accounts, and audits against the standards the company must meet. |
Alongside the technical controls sit the human ones: a written policy that staff acknowledge, onboarding and offboarding steps that create and remove accounts, training, and a managed exception process. See Microsoft's pages on banned-password protection and password policies in Entra ID.
Where a generator fits in
A policy says what a password must look like. A generator produces ones that
meet it without a human inventing them. If your policy still demands a mix of
character types, use the exact-count mode to satisfy it; if it follows the
newer length-first guidance, generate something long, such as
[A-Za-z0-9]{24}. Either way, store the result in a vault and never
reuse it.
Frequently asked questions
Can a regex password generator guarantee at least one uppercase letter, digit and symbol?
Not from a pattern alone, because the generator does not support lookaheads. You can write the structure out instead, for example [A-Z][a-z]{6}[0-9]{3}[!@#$%], but then each character type sits in a fixed position. If you just need at least one of each type anywhere in the password, use the Length and characters mode: every ticked type is guaranteed at least one character and the characters are shuffled.
Is a password generated from a regular expression less secure?
It is exactly as strong as the number of different passwords the pattern allows. Each character drawn from a set of N options adds log2(N) bits, and fixed text adds none. [A-Za-z0-9]{16} allows 62 to the power of 16 passwords, about 95 bits. [0-9]{6} allows a million, about 20 bits. The characters themselves come from the browser's cryptographic random number generator, crypto.getRandomValues.
Is my pattern or the generated password sent to a server?
No. The pattern is read and the password is built entirely in your browser. Nothing is sent, logged or stored by the site.
Which regular expression features does the generator support?
Literals, character classes such as [a-z] and [^0-9], the shorthands \d, \w and \s, the dot, groups ( ) and (?: ), alternation with |, and the repeats ?, *, +, {n}, {n,} and {n,m}. Lookaheads, lookbehinds, backreferences, named groups, word boundaries and flags are rejected with a message, and ^ and $ are only accepted at the very start and end of the pattern.
Why does [a-z]+ give me a different length each time?
Open-ended repeats (*, + and {n,}) are capped at 8 extra repeats, so [a-z]+ produces between 1 and 9 letters. If you want a fixed length, say so with {n}, for example [a-z]{12}. The page shows the length of every generated password.
What is a strong password policy?
A password policy is the set of rules an organisation applies to how passwords are created, stored, changed and protected. A strong one sets a sensible minimum length, bans common and breached passwords, forbids reuse, limits failed attempts, requires multi-factor authentication for remote and admin access, and treats service and shared accounts separately with generated, vaulted, rotated passwords.
How do enterprises enforce password policies?
In the systems people log in to. Directory and identity services such as Active Directory and Microsoft Entra ID reject non-compliant passwords when they are set or changed, banned-password features check new passwords against lists of weak and breached values, lockout and rate limits slow guessing, conditional access makes multi-factor authentication mandatory, and privileged-access vaults generate and rotate passwords for service and admin accounts. Audits and monitoring check that it all stays in force.
Do companies still have to force password changes every 90 days?
Not under current NIST guidance (SP 800-63B revision 4), which recommends changing a password when there is evidence of compromise rather than on a fixed schedule, and favours length and blocklist checks over composition rules. Some organisations and other frameworks still set their own expiry rules, so check the standards that apply to you.
Is a long password enough on its own?
No. A long random password defeats guessing, but it does not help if the same password is reused on another site that gets breached, or stolen by malware. The Colonial Pipeline VPN password was reported as relatively complex yet reused, on an account with no multi-factor authentication. Use a unique generated password for every account and add multi-factor authentication.
How can sysadmins use a password generator with patterns?
To match a policy or a system's quirks exactly: letters and digits only for software that rejects symbols, a fixed length for a field limit, a dashed format for keys read aloud, or a set without look-alike characters such as [A-HJ-NP-Za-km-z2-9]{16}. Use exact counts when a policy demands a specific mix, and store the result in a password manager or vault rather than pasting it into a ticket.
Can I choose exactly how many digits or symbols the password has?
Yes. In Length and characters mode each ticked character type has a number box beside it. Set 6 uppercase, 6 lowercase, 4 digits and 4 symbols for a 20-character password, for instance. The total can never exceed the length you chose; if your numbers add up to more, the largest count is trimmed, and if they add up to less, the gap is filled at random.
Related: Strong Password Generator · Passphrase Generator · What Is a Passphrase? · Regular Expression for an IP Address